Iran - Israel/US War: Israel-US declare war on Iran, Iran responds

All those worldwide cyberattacks and power outages.

A lot of countries are urging the people to secure enough food and water at home.

US militairy bases are excercising for grid malfunctions.

International Power Outage is coming 17 november.

No internet, no electricity.
 
🇮🇷🛢 Iran Prepares “Zero Oil” Budget Scenario to Withstand US Blockade

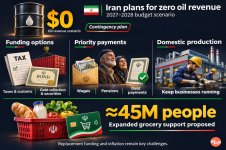
Iran is preparing its 2027–2028 budget for a scenario in which oil revenues fall to zero, seeking to keep salaries, pensions and essential services funded under US sanctions and blockade.

Mohammad Ghasemi, a senior official at Iran’s Plan and Budget Organization, outlined the approach in remarks published November 9. The Persian year 1406 budget will examine several scenarios, including a complete loss of oil income, rather than assume export earnings will recover.

The financing options include taxes, customs receipts, collecting outstanding debts and issuing debt securities. Oil deposit certificates are also under consideration. These measures would help cover the shortfall, but their inclusion in emergency planning does not establish that Iran can already replace every dollar of lost oil revenue.

Spending would follow a strict order, with public wages, pensions and debt repayments taking priority. Other expenditure would depend on available funds, while infrastructure money would concentrate on projects that can actually be completed and put to use.

Domestic production is central to the approach because Iran supplies many of its own needs and pays a substantial share of its costs in rials. Keeping businesses running protects jobs, goods supplies and tax receipts. The government therefore intends to avoid excessive tax pressure on war-damaged petrochemical and steel businesses, as well as struggling tourism firms.

Ghasemi said the government had so far avoided direct central bank borrowing for the general budget. That claim has a narrower scope than a blanket rejection of monetary support, since he also acknowledged central bank assistance to smooth payments under the household voucher program.

Officials are seeking funding to increase electronic grocery-voucher support for roughly 45M low-income people and raise wage earners’ tax exemptions. Proposed reforms to energy use and wheat, flour and bread distribution aim to reduce waste and smuggling while protecting household access to essentials.

The objective is to make an oil cutoff less effective at disrupting everyday government functions. If Iran can fund essential payments while preserving domestic production, Washington’s ability to turn lost export earnings into shuttered businesses and unpaid wages would weaken. That depends on securing replacement revenue and containing inflation.

@NewRulesGeo❗Follow us on X
 

Attachments

  • IMG_20261111_110621_910.jpg
    IMG_20261111_110621_910.jpg
    198.6 KB · Views: 2
You need to buy a VPS inside Iran and install a VPN server on it on your own.
Nobody is going to share one with you for legal reasons, unfortunately.
Watch out, if you hack a French fridge from there, DGSE dumbfucks would make a diplomatic conflict, for them it's enough ip address as evidence of Iran involvement in hacking.
 
Watch out, if you hack a French fridge from there, DGSE dumbfucks would make a diplomatic conflict, for them it's enough ip address as evidence of Iran involvement in hacking.
Their excuse was even more stupid than the IP addresses of the hackers.
They said the malware had codes written in Persian lol

Who writes code in Persian? I cannot, for the life of me, even think that somebody writes C/C++ or whatever other language in Persian lol
 
Their excuse was even more stupid than the IP addresses of the hackers.
They said the malware had codes written in Persian lol

Who writes code in Persian? I cannot, for the life of me, even think that somebody writes C/C++ or whatever other language in Persian lol
The comments of the code, not the code itself
 
You need to buy a VPS inside Iran and install a VPN server on it on your own.
Nobody is going to share one with you for legal reasons, unfortunately.
There is an app in play store called Iran IP connect that allows u to connect to Iranian sites
 
The comments of the code, not the code itself
But who leaves comments when developing a malware?
The whole thing is stupid.

And by the way, I'm pretty sure even Iranian programmers write comments inside their codes in English, even if it's broken English. It's like a universal thing.
 
Their excuse was even more stupid than the IP addresses of the hackers.
They said the malware had codes written in Persian lol

Who writes code in Persian? I cannot, for the life of me, even think that somebody writes C/C++ or whatever other language in Persian lol
the official excuses are both things, ip address from iran and Persian words in the code 😂.

I dont doubt french are saying truth, i doubt about their stupid conclusion.

Replace all Persian words in any code is a few sed commands in linux terminal.

So the real authorship seems pretty clear if the attacker wants to point to Iran.

The troublemaker tribe of always: 🇮🇱

A sadistic stupid attack that we are used to from those people, and the expected reaction of unworthy french vassals lying to own people to please American masters, the common in this decadent Europe.
 
the official excuses are both things, ip address from iran and Persian words in the code 😂.

I dont doubt french are saying truth, i doubt about their stupid conclusion.

Replace all Persian words in any code is a few sed commands in linux terminal.

So the real authorship seems pretty clear if the attacker wants to point to Iran.

The troublemaker tribe of always: 🇮🇱

A sadistic stupid attack that we are used to from those people, and the expected reaction of unworthy french vassals lying to own people to please American masters, the common in this decadent Europe.
Nobody leaves comments inside a malware. Why would they?

// This line is the part that installs a backdoor.

I mean why would they do that? Also, comments show up unaltered when you reverse engineer the binary file. So, again, why would a hacker do that?

The whole thing is stupid and it is obviously not true. But it just shows you how easy it has become for European officials to lie to the public.
 
I guess not building a air force and building the under ground missile bases was after all a genius plan by Iran

what a master class stroke by Iran

outplayed two Global Superpowers with Nukes and came out on top

Iran should now demand full compensation and US needs to bend its knee and accept

but I know US has more blunders to make yet
 
Nobody leaves comments inside a malware. Why would they?

// This line is the part that installs a backdoor.

I mean why would they do that? Also, comments show up unaltered when you reverse engineer the binary file. So, again, why would a hacker do that?

The whole thing is stupid and it is obviously not true. But it just shows you how easy it has become for European officials to lie to the public.
Nobody leaves comments inside a malware, besides those who want to make the victim believe X did the attack
 

Users who are viewing this thread

Pakistan Defence Latest

Latest Posts

Back
Top