Nvidia faces ransom demands from The Gentlemen: countdown timer leaves less than 10 days
The group has not provided any evidence to substantiate the claim.
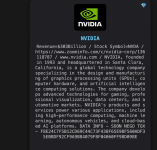
The Gentlemen data leak site, screenshot.
Cybernews researcher Aras Nazarovas noted that The Gentlemen had previously exaggerated claims, misattributed targeted companies, and even used recycled stolen data.
What do we know about the Gentlemen?
The Gentlemen emerged as a ransomware-as-a-service group around July 2025, and rapidly rose to prominence as one of the most active ransomware gangs. The threat actor offers its affiliates a 90% share of ransom payments and has claimed 1,123 victims in 95 countries to date, according to the Ransomware.live tracker.
Security researcher and journalist Brian Krebs previously reported that the group’s administrator, known as Zeta88 and Hastalamuerte, is believed to be based in Russia. The Gentlemen rely on AI to develop and maintain their ransomware and tools, and assist with post-exploitation.
According to a Barracuda
report, The Gentlemen evolved from an affiliate operation previously called ArmCorp, which had previously worked with the Qilin ransomware ecosystem. The group uses Russian-language communications, recruits on Russian-speaking forums, and reportedly avoids targeting organizations in the Commonwealth of Independent States (CIS), but the researchers haven’t found evidence of any nation-state collaboration.
Some of the gang’s previous victims include
NATO contractor Indra,
European data exchange platform FTAPI,
Dutch ice arena Thialf,
LA Metro,
Glassdoor,
MoneyGram, and others.
Recently, the Gentlemen’s affiliate was found to be running its own operation, secretly hijacking victims and
cutting the ransomware gang out of its payday.